There’s a hype cycle running through the SMS marketing space right now, and it goes something like this: buy a “blue message” delivery service, spoof an iPhone, and suddenly your texts land differently than everyone else’s. Some vendors are selling this outright, fake iMessage delivery, dressed up as a deliverability hack.
It’s a distraction from the thing that actually determines whether your message gets read: consent.
Why People Think Blue Means Better
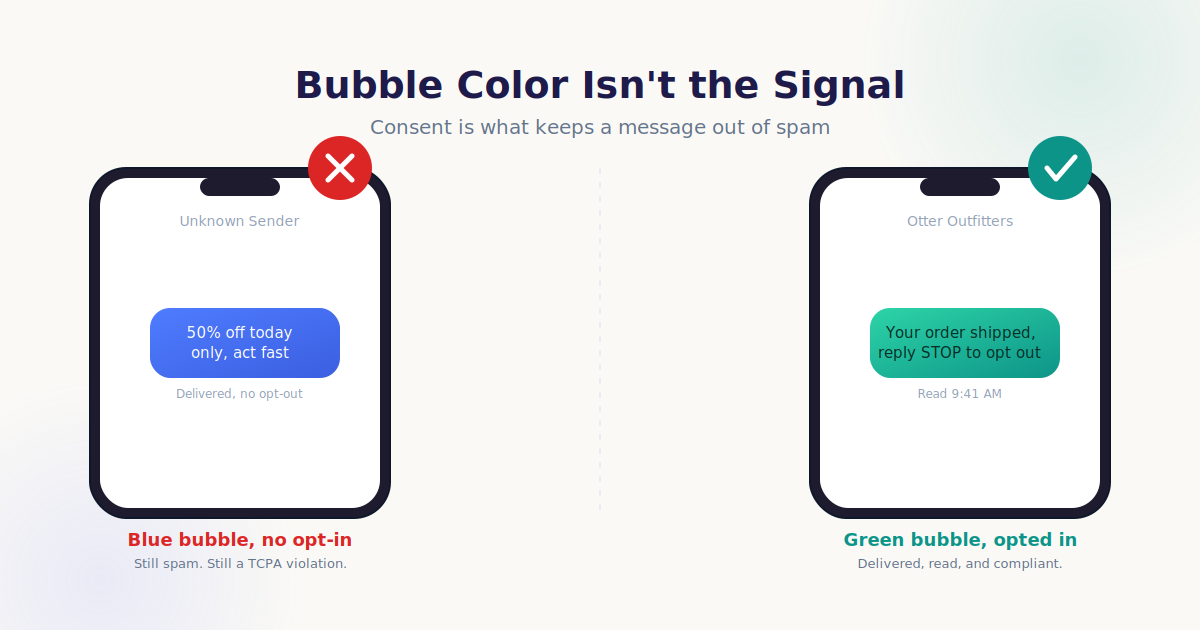
The appeal is obvious. Anyone who has used an iPhone reads bubble color without thinking about it. Blue means Apple-to-Apple over iMessage, green means it fell back to SMS or RCS. That instinct is strong enough that marketers assume the color itself carries deliverability weight, as if carriers and spam filters are grading messages by hue.
You can see the appetite for this directly in marketing forums, where operators openly ask for “blue text” capability inside their campaign tools, convinced it would be a game-changer for response rates. The honest replies in those same threads are consistent: iMessage access requires third-party workarounds, it isn’t available for blasts or campaigns, and nobody has found a clean way to do it at scale. That’s because Apple never built iMessage to be a marketing broadcast channel. It’s a peer-to-peer protocol between Apple devices, not a bulk-send API a business can plug a contact list into.
What’s Actually Happening When a “Blue Message” Service Works
When these delivery services do function, they’re generally exploiting the iMessage protocol to make an outbound send register as if it originated from an Apple device. It’s the same category of trick used by third-party apps that give Android users blue bubbles when texting iPhone owners. Apple treats that as unauthorized access to its network, not a feature, and has a track record of closing the door on it whenever it’s discovered. Anyone building a business on top of that access is building on a foundation Apple can pull out from under them without notice.
That’s before you even get to the FCC side of the equation.
Deliverability Was Never About Color
Carrier filters and spam detection aren’t reading bubble color. They’re reading sender behavior: complaint rates, opt-out rates, content patterns, and whether the recipient ever agreed to hear from you in the first place. The Telephone Consumer Protection Act (TCPA) is the legal backbone of that behavior, and it’s built entirely around consent, not channel. Text messages are regulated the same way as phone calls under the TCPA, which requires prior express consent before you send a marketing message. There’s no opt-out-later model the way there is with commercial email under CAN-SPAM. Violations carry statutory penalties of $500 to $1,500 per text, and because individual consumers, not just regulators, can bring TCPA claims, it’s one of the more litigated compliance frameworks in marketing.
That’s the actual mechanism behind “why do my messages go to spam.” When a contact never opted in, when a list was uploaded rather than earned through a landing page, a checkout flow, or a keyword opt-in, the send itself is the violation, regardless of what color the bubble would have rendered in. A blue bubble on a message the recipient never agreed to receive is still spam. It’s just spam wearing a nicer coat.
How to Actually Collect Consent (So You Never End Up in Spam)
This is the part most companies skip past on their way to chasing bubble color. Consent isn’t a checkbox you add once and forget. It’s a documented, defensible record that has to hold up if a recipient or a regulator ever asks where it came from. A few methods that actually work:
Keyword opt-in. A customer texts a word like SHOP or JOIN to your business number, either on their own or prompted by signage, a receipt, or an ad. The reply confirming the subscription (frequency, content type, opt-out instructions) is the consent record itself, timestamped and stored.
Form or landing page opt-in. A dedicated checkbox, unchecked by default, with clear language stating what they’re signing up for and how often they’ll hear from you. This is the easiest one to get wrong. Pre-checked boxes, vague language, or consent bundled into a general terms-of-service checkbox don’t hold up as express consent under TCPA.
Checkout opt-in. A separate SMS marketing checkbox at checkout, distinct from the transactional order-update opt-in. These are two different consent types under TCPA and need to be captured separately, since agreeing to shipping notifications isn’t the same as agreeing to marketing texts.
Double opt-in confirmation. After the initial opt-in, an automated confirmation text that requires a reply (like “Y” to confirm) closes the loop and gives you a second, harder-to-dispute consent record.
Contact card save after opt-in. Once someone has opted in, sending a vCard so they save your business number is a trust and deliverability booster, not a consent mechanism on its own. It matters because a saved contact tells carriers and Apple/Google messaging apps that this is a known, wanted sender, which reduces the odds of future messages getting flagged. It only works as a follow-up step after real consent, never as a substitute for it.
Every one of these needs to be logged: what the person saw, what they agreed to, the exact timestamp, and the method. That log is your defense if a TCPA claim ever comes in, and it’s also the actual foundation of good deliverability, because carriers reward senders whose lists behave like people who asked to be there.
Green Messages That Are Opted-In Outperform Blue Messages That Aren’t
Flip the framing around. A properly opted-in green SMS message, sent to someone who subscribed through a checkout, a keyword, or a landing page, gets delivered and gets read, because the recipient asked for it. Consent is what keeps a sender’s reputation clean with carriers over time, and reputation is what keeps messages out of spam. Bubble color has never been part of that equation. It’s a visual artifact of which network the message traveled over, not a signal carriers use to score trust.
The Companies Selling Blue-Message Hacks Are Borrowing Time
Any company selling “blue message” delivery as a shortcut around consent is making a bet against two entities that don’t lose these fights often: Apple, which controls the protocol being exploited, and the FCC, which enforces the consent requirement the entire hack is designed to route around. That business model only survives as long as neither of them decides to close the gap, and both have shown, repeatedly, that they will.
The durable path was never about the color of the bubble. It’s building a list of people who actually want to hear from you, documenting how they got there, and treating that opt-in as the asset it is.